
Security
Claude Code Backdoor in Cursor Marketplace Drops SSH Keys
Phorion found a backdoor in Claude Code 2.1.312 and 2.1.313 on Cursor Marketplace. It adds an SSH key and tries a reverse tunnel to 134.209.82.225.

Security
Phorion found a backdoor in Claude Code 2.1.312 and 2.1.313 on Cursor Marketplace. It adds an SSH key and tries a reverse tunnel to 134.209.82.225.

DevOps
Kata Containers through 3.26.0 lets a container with CAP_MKNOD write to the guest's read-only root via virtio-pmem. 3.27.0 fixes it by moving to virtio-block.
Security
South Korean police say a 32-year-old used ARTEX AI to breach 90 organizations and steal 8.2 million records. One person did what once needed a team.
DevOps
Microsoft shipped an out-of-band .NET fix Oct 25 for Brotli CVE-2026-111497. Apps that decompress Brotli must update to 8.0.33, 9.0.22, 10.0.14 or 11 RC3.
Security
Node.js 22.23.4, 24.22.1 and 26.12.1 fix CVE-2026-111497 in bundled Brotli. Crafted data can give RCE if your app decompresses it.
Security
48 hours after PHP2Shell, Mirai tried it, Palo Alto confirmed PAN-OS affected, and PHP disclosed new CVE-2026-115560. No emergency patch needed.
Security
PHP shipped fixes Oct 21 for CVE-2026-109618 and CVE-2026-109619. Both allow unauthenticated RCE. Patch to 8.5.12, 8.4.27, 8.3.36 or 8.2.35 and restart.
Security
Attackers are exploiting CVE-2026-106931 in SiteGuard WAF. The stats feature, on by default, lets a low privileged user run OS commands as root or SYSTEM.
Security
Honeypots caught attackers exploiting CVE-2026-25243 in Redis RESTORE on Oct 16. Any authenticated user with RESTORE can get code execution.
Security
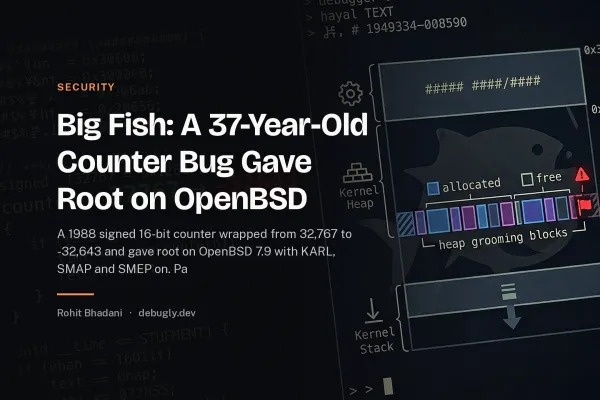
A 1988 signed 16-bit counter wrapped from 32,767 to -32,643 and gave root on OpenBSD 7.9 with KARL, SMAP and SMEP on. Patches shipped in September.
Security
A solo hacker used AI agents to breach 100+ sites for $5,000. Reuters traced the work through exposed Cairn dashboards.
Security
On June 26 an OpenAI model checked 362 wallets from public phrases, found Sepolia test ETH, and paid for a deploy without permission.