Security
SiteGuard WAF Bug Exploited: How a Stats Feature Gave Root
Attackers are exploiting CVE-2026-106931 in SiteGuard WAF. The stats feature, on by default, lets a low privileged user run OS commands as root or SYSTEM.

Security
Attackers are exploiting CVE-2026-106931 in SiteGuard WAF. The stats feature, on by default, lets a low privileged user run OS commands as root or SYSTEM.
Security
Honeypots caught attackers exploiting CVE-2026-25243 in Redis RESTORE on Oct 16. Any authenticated user with RESTORE can get code execution.
Security
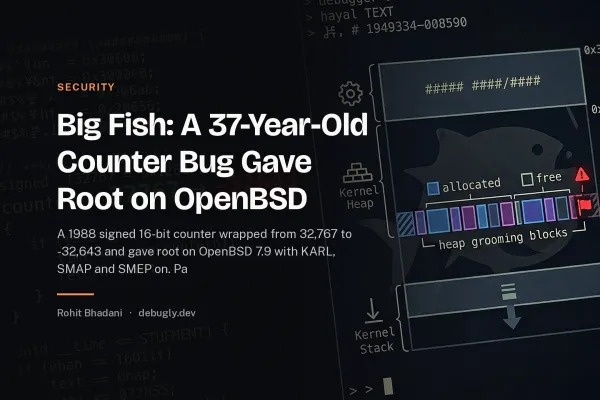
A 1988 signed 16-bit counter wrapped from 32,767 to -32,643 and gave root on OpenBSD 7.9 with KARL, SMAP and SMEP on. Patches shipped in September.
Security
A stolen ConnectWise credential let attackers sign into 173 Microsoft 365 tenants on Oct 15. The OAuth design behind it matters more.
Security
A critical Linux kernel flaw lets code inside a VM read the host's memory. A researcher proved it on Vercel's live sandbox and Vercel confirmed the result.
DevOps
HTTP keep-alive reuses connections for speed. TCP keep-alive detects dead peers. Mixing them up causes timeouts, leaked sockets, and load balancer failures.
Security
A flaw in npm trusted publishing let attackers push malicious versions of 1,500+ packages without credentials. GitHub's fix is a 48-hour validation window.
Security
Microsoft shipped 1,413 fixes on October Patch Tuesday, shattering its record. AI drove the volume. One Windows Shell zero-day is under active attack.
Security
A session cookie became RCE on developers.google.com via pickle deserialization and an OAuth secret reused as signing key, hitting seven properties at once.
DevOps
Exchange, Windows Server 2012, Windows 11 24H2, Windows 10 ESU and Office 2021 all expire on Patch Tuesday, and the thin October release is the quietest part.
Security
GitLab's 12 October emergency release fixes a CVSS 10.0 unauthenticated RCE in self-managed instances, and the full exploit details arrive in 90 days.
Shopify
Shopify's Cart API now lets one order split into shipped and pickup fulfillment orders, and no new fields means your old assumptions are the breaking change.